
About This Launch
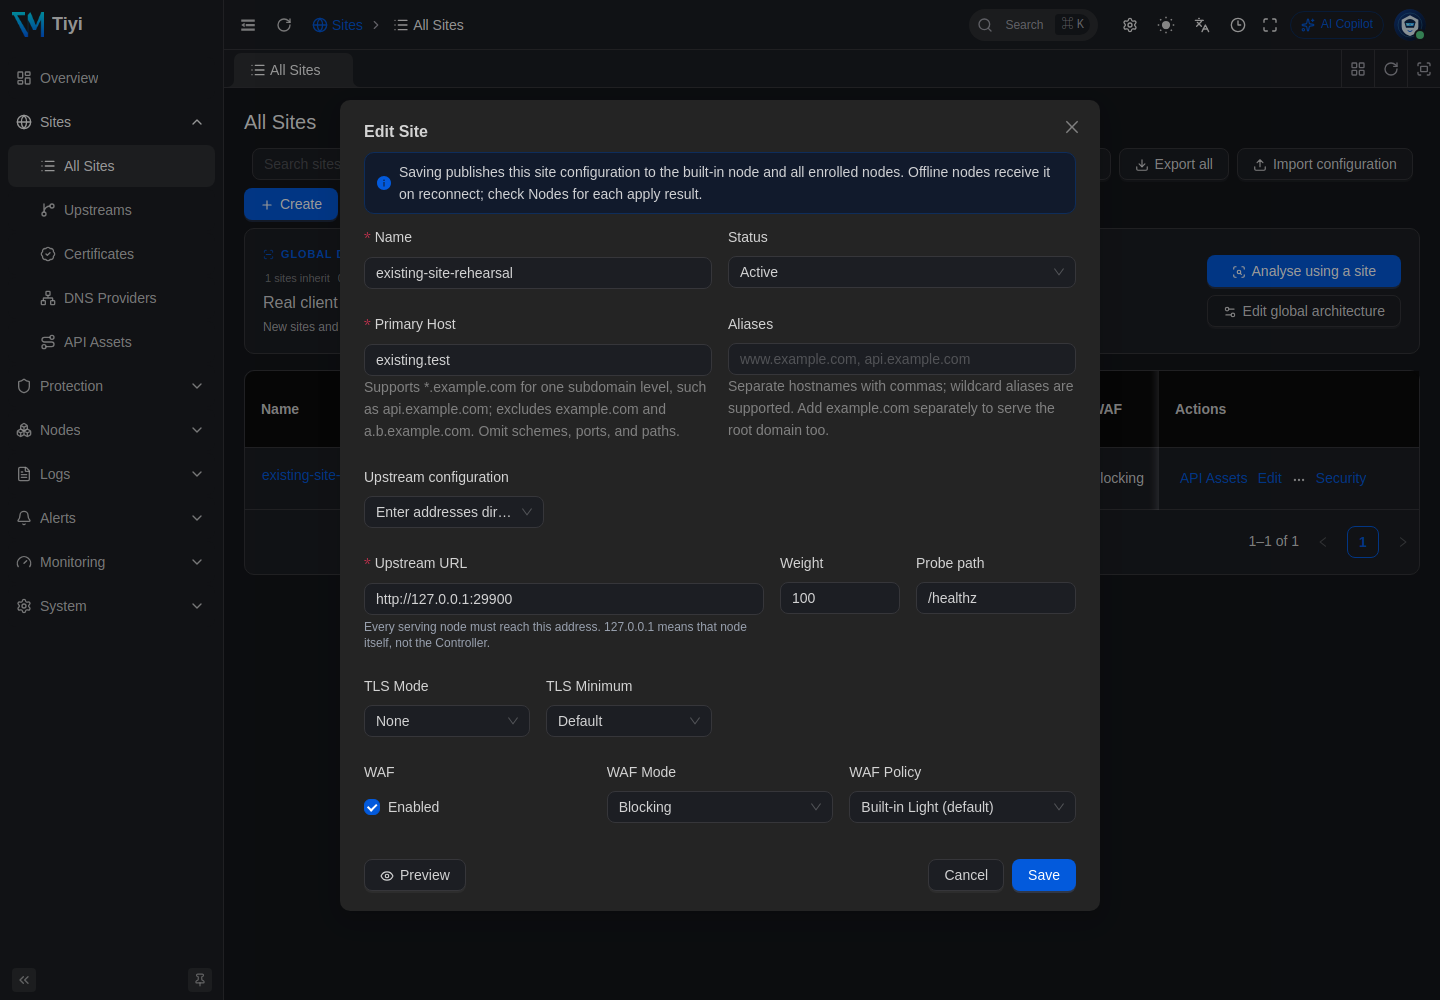
Tiyi is a self-hosted web application firewall and reverse proxy for websites and APIs. One Linux binary includes the proxy, OWASP CRS-based protection, an admin UI, and SQLite storage, no Docker or external database needed. Operators can place it behind an existing Nginx site, inspect blocked requests, and tune narrow rule exceptions. The local single-node feature set is free; multi-node management requires a license.
Screenshots
Why I Built This
Existing site operators need a way to add WAF protection without replacing their application or losing a clear recovery path. Tiyi brings the proxy, WAF and management UI into one installable binary, with per-site rule tuning.
Launch Details
CategoryDeveloper Tools
StageLive
ListedSeptember 25, 2026